西维蜀黍

【Redis】数据类型的底层数据结构 - String

  ...


【Redis】数据类型的底层数据结构 - ZSet

跳跃表(跳表,Skiplist)

引言

Redis因为其完全基于内存、性能出色,加上具备丰富的数据类型,在电商环境中深受后端开发的喜爱。其中有序集合zset就是基本数据类型之一,并且每个member都带有score(可用于排序),因此很适合在打赏日榜、近一周收益这类场景中运用。

跳表的定义

跳表:增加了向前指针的链表叫做指针。跳表全称叫做跳跃表,简称跳表。跳表是一个随机化的数据结构,实质是一种可以进行二分查找的有序链表。跳表在原有的有序链表上增加了多级索引,通过索引来实现快速查询。跳表不仅能提高搜索性能,同时也可以提高插入和删除操作的性能。

跳表是一个随机化的数据结构,可以被看做二叉树的一个变种,它在性能上和红黑树、AVL树不相上下,但是跳表的原理非常简单,目前在Redis和LevelDB中都有用到。

  ...


【Hackintosh】硬件购买指南

网卡

Ref

  ...


【Golang】Prepared Statements in Golang

Background

What is a prepared statement?

A prepared statement is SQL that is parsed and saved by the DBMS, typically containing placeholders but with no actual parameter values. Later, the statement can be executed with a set of parameter values.

  ...


【MySQL】Prepared Statements

Prepared Statements

MySQL 8.0 provides support for server-side prepared statements. This support takes advantage of the efficient client/server binary protocol. Using prepared statements with placeholders for parameter values has the following benefits:

  • Less overhead for parsing the statement each time it is executed. Typically, database applications process large volumes of almost-identical statements, with only changes to literal or variable values in clauses such as WHERE for queries and deletes, SET for updates, and VALUES for inserts.
  • Protection against SQL injection attacks. The parameter values can contain unescaped SQL quote and delimiter characters.

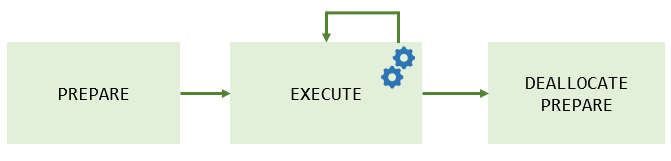
In order to use MySQL prepared statement, you use three following statements:

  • PREPARE – prepare a statement for execution.
  • EXECUTE – execute a prepared statement prepared by the PREPARE statement.
  • DEALLOCATE PREPARE – release a prepared statement.

The following diagram illustrates how to use a prepared statement:

  ...


【Security】SQL Injection

SQL 注入(SQL Injection)

Overview

A SQL injection attack consists of insertion or “injection” of a SQL query via the input data from the client to the application. A successful SQL injection exploit can read sensitive data from the database, modify database data (Insert/Update/Delete), execute administration operations on the database (such as shutdown the DBMS), recover the content of a given file present on the DBMS file system and in some cases issue commands to the operating system. SQL injection attacks are a type of injection attack, in which SQL commands are injected into data-plane input in order to affect the execution of predefined SQL commands.

SQL 注入漏洞(SQL Injection)是 Web 开发中最常见的一种安全漏洞。可以用它来从数据库获取敏感信息,或者利用数据库的特性执行添加用户,导出文件等一系列恶意操作,甚至有可能获取数据库乃至系统用户最高权限。

而造成 SQL 注入的原因是因为程序没有有效的转义过滤用户的输入,使攻击者成功的向服务器提交恶意的 SQL 查询代码,程序在接收后错误的将攻击者的输入作为查询语句的一部分执行,导致原始的查询逻辑被改变,额外的执行了攻击者精心构造的恶意代码。

很多 Web 开发者没有意识到 SQL 查询是可以被篡改的,从而把 SQL 查询当作可信任的命令。殊不知,SQL 查询是可以绕开访问控制,从而绕过身份验证和权限检查的。更有甚者,有可能通过 SQL 查询去运行主机系统级的命令。

  ...


【Design Pattern】Structural - Facade

  ...


【Design Pattern】Transformer

Transformers

Transformers contain the business logic for changing a model’s format to whatever you need for the output, whether that’s HTML, Datatable, or JSON API. Decoupling this logic from the model allows for unobtrusive schema changes, a reliable place for housing formatting logic, and data formatting operations outside of views (for example, converting a date, or performing translations).

  ...


【Engineering】Chaos-Engineering

  ...


【Engineering】SLO and SLA

SLO(Service Level Objective,服务水平目标)和SLA(Service Level Agreement,服务水平协议)是服务管理中的两个重要概念,它们之间有着明显的区别:

  1. 定义:
    • SLO:这是具体的性能目标,如系统的可用性、响应时间或处理能力等。它们是量化的指标,用于衡量服务的性能和可靠性。
    • SLA:这是服务提供商和客户之间的正式协议。它包含多个SLO,还可能包括对于服务质量的承诺、违约责任、服务时间等。
  2. 功能和目的:
    • SLO:是服务提供者内部用来确保其服务达到预期标准的具体目标。SLO帮助团队专注于重要的性能指标。
    • SLA:是一种法律文件,规定了服务提供者必须达到的最低服务标准以及未能达到这些标准时的后果。它为客户和服务提供商之间的关系提供了法律框架。
  3. 范围和细节:
    • SLO:更为具体和量化,专注于单个性能指标。
    • SLA:范围更广,不仅包括性能指标,还包括服务的所有其他方面,如客户支持、报告要求等。

简而言之,SLO是SLA的一部分,它们共同帮助确保服务提供者能夠满足客户的期望和需求。SLA提供了一个全面的服务框架,而SLO则是在这个框架内,具体衡量服务性能的标准。

  ...